Security built around protecting your data.
BotNira is designed with security controls covering data transmission, storage, access, infrastructure, monitoring, vulnerability management and incident response.
Multiple layers of protection across the BotNira platform.
Security is part of the platform, not an afterthought.
BotNira handles business and customer communication data across voice calls, WhatsApp, email, website chat and other supported workflows.
Our security program is designed to protect this information throughout its lifecycle — from transmission and authentication through storage, processing, monitoring and deletion.
Security controls are combined with regional data-residency architecture so that customer data is stored according to the applicable BotNira regional environment.
Multiple layers of security
BotNira uses multiple technical and organizational controls rather than relying on a single security mechanism.
🔒 Encryption
Data is protected through encryption controls both while being transmitted and while stored.
🛡️ Network Protection
Firewall and DDoS protection help defend BotNira infrastructure against unauthorized and malicious network traffic.
🔑 Authentication
Two-factor authentication provides an additional layer of protection for supported account access.
🔍 Vulnerability Management
Regular vulnerability scanning is performed to identify potential weaknesses.
🧪 Penetration Testing
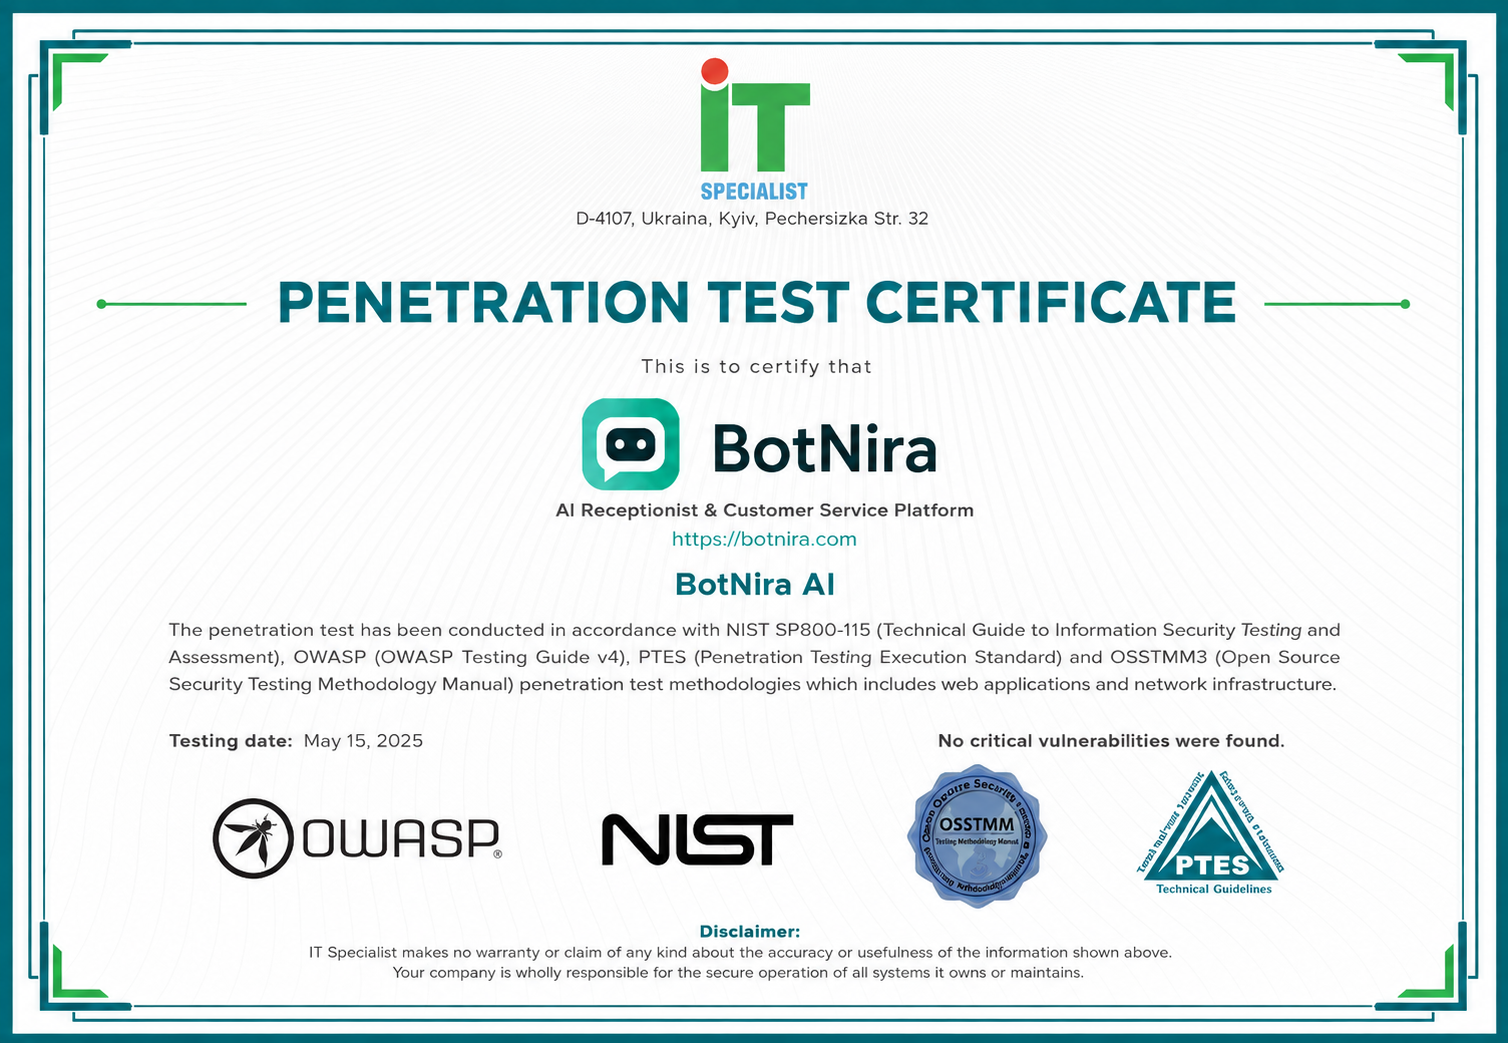
Penetration testing has been completed as part of the BotNira security program.
🚨 Incident Response
A dedicated security team is responsible for responding to security incidents.
Security controls protecting BotNira
The following controls form the core of BotNira's technical security architecture.
SSL / TLS
Secure TLS connections are used to protect information transmitted between users, applications and BotNira services.
Encryption at Rest
Stored information is protected using encryption controls designed to reduce the risk of unauthorized access.
Encryption in Transit
Information transmitted across supported communication channels is protected through encrypted connections.
Two-Factor Authentication
2FA provides an additional authentication factor to help protect supported BotNira accounts.
Firewall Protection
Network firewall controls help restrict unauthorized network traffic and protect infrastructure.
DDoS Protection
DDoS protection helps mitigate malicious traffic designed to overwhelm services.
Database Backups
Regular database backups support resilience, recovery and protection against data loss.
Vulnerability Scanning
BotNira performs regular vulnerability scanning to identify potential security weaknesses.
Penetration Testing
Penetration testing has been completed to evaluate security defenses and identify potential weaknesses.
Internal Data Access
Customer data is not accessible to members of the BotNira team as part of ordinary operational activities.
Security Team
A dedicated security team is responsible for security monitoring and incident response.
Data Deletion
Following account closure, applicable data is retained for up to 45 days and then permanently deleted according to BotNira's retention policy.
Access to customer data is restricted.
BotNira follows a restricted-access approach for customer information.
Members of the BotNira team do not have ordinary access to customer data as part of their normal day-to-day operations.
This reduces the number of people who can interact with customer information and forms part of BotNira's overall security architecture.
Security across the data lifecycle
Transmission
Data transmitted between supported systems is protected through encrypted connections.
Processing
BotNira processes information through its application and applicable integrated providers required to deliver specific functionality.
Storage
Customer data is stored within the appropriate BotNira regional environment based on the vendor's region.
Backup
Regular backups support service resilience and recovery. Regional data-residency commitments apply to applicable vendor data.
Monitoring
Security monitoring and vulnerability management help identify potential security issues.
Deletion
Following account closure, applicable data is retained for up to 45 days before permanent deletion.
Regional storage is part of our security model.
BotNira operates regional environments so that vendor data is stored according to its applicable geographic region.
🇨🇦 Canada
Canadian vendor data is stored and backed up within the Canadian regional environment.
View Canada →🇺🇸 United States
U.S. vendor data is stored and backed up within the U.S. regional environment.
View United States →🇪🇺 Europe
European vendor data is stored and backed up within the European regional environment.
View Europe →🇬🇧 United Kingdom
UK vendor data is stored and backed up within the UK regional environment.
View United Kingdom →🇦🇺 Australia
Australian vendor data is stored and backed up within the Australian regional environment.
View Australia →🇮🇳 India
Indian vendor data is stored and backed up within the Indian regional environment.
View India →Testing and continuous security improvement
Security is an ongoing process. BotNira performs regular vulnerability scanning and has completed penetration testing as part of its security program.
Findings from security activities can be used to identify areas for remediation and improve the overall security posture of the platform.
Independent security and compliance evidence
BotNira maintains the following certificates and assessment documentation as part of its broader security and compliance program.
HIPAA documentation
BotNira maintains HIPAA-related certification documentation as part of its security program.
However, a certificate alone does not mean that every BotNira customer automatically has a HIPAA-covered arrangement.
At present, BotNira does not represent that it has entered into a Business Associate Agreement (BAA) with every customer. Healthcare customers with HIPAA requirements should contact BotNira before using the service for regulated PHI.
Responding to security incidents
BotNira maintains a security response process for identifying, investigating and responding to security incidents.
Detection
Security monitoring and vulnerability-management activities can help identify potential security issues.
Investigation
Reported or identified security events can be investigated by the security team.
Containment
Appropriate technical and operational measures may be taken to contain identified threats.
Remediation
Identified security issues are addressed through appropriate corrective actions.
Security includes responsible deletion.
BotNira does not retain customer data indefinitely after an account is closed.
When a vendor stops using BotNira and closes its account, applicable data is retained for 45 days .
After the applicable 45-day period, the data is permanently deleted according to BotNira's retention process.
While an account remains active, vendors can manage and delete their customer calls, messages and related data using available BotNira functionality.
Know who is involved in your data flow.
BotNira provides transparency about third-party providers involved in communication and AI functionality.
Twilio
Provides telephone connectivity and acts as the communication bridge for applicable voice services.
Meta / WhatsApp
Provides WhatsApp communication infrastructure for applicable messaging services.
OpenAI
Provides AI services used for applicable BotNira AI-powered processing.
Security documentation
Additional security and compliance information is available throughout the BotNira Trust Center.
Data Residency
Understand where BotNira stores vendor and customer data by region.
View Data Residency →Subprocessors
Review third-party providers used to provide BotNira functionality.
View Subprocessors →Have a security concern?
Security-related questions or concerns can be directed to the BotNira security team.
Frequently asked security questions
Does BotNira encrypt data?
Does BotNira use two-factor authentication?
Does BotNira perform penetration testing?
Does BotNira regularly scan for vulnerabilities?
Can BotNira employees access my customer data?
How long does BotNira retain data after account closure?
Where is my data stored?
Does BotNira use third-party providers?
Does having a HIPAA certificate mean I can automatically use BotNira for PHI?
How can I contact BotNira about security?
Certifications and assessments should be reviewed according to their individual scope, validity period and applicable terms.
Security, transparency and control.
Explore BotNira's regional data residency, subprocessors, AI processing and privacy documentation.