Australia Data Residency
BotNira provides Australian vendors with regional data storage and backups while supporting AI-powered communication and customer service.
Customer data is stored in Australia.
Australian vendor data stays in Australia
When a business located in Australia signs up for BotNira, that business is treated as an Australian vendor for data-residency purposes.
BotNira stores the vendor's BotNira data in its Australian regional infrastructure. Backups for Australian vendor data are also maintained in Australia.
This regional approach is designed to provide Australian businesses with a dedicated local storage environment while still allowing BotNira to provide its AI-powered services.
How Australian data moves through BotNira
BotNira separates regional data storage from external services used for specific communication and AI functionality.
Phone Calls
Twilio provides telephone connectivity and acts as the communication bridge between the customer's telephone network and BotNira.
Speech and AI processing may be performed through OpenAI services.
WhatsApp provides the messaging infrastructure used to transmit messages between customers and BotNira.
Where AI processing is required, relevant message content may be processed through OpenAI services.
Email communication is handled directly through BotNira infrastructure.
OpenAI may be involved when an AI-powered feature requires processing of email content.
Website Chat
Website chat is provided and managed directly by BotNira without a separate messaging intermediary.
OpenAI may process content when an AI-powered feature requires it.
Built with Australia's privacy principles in mind
Australia's Privacy Act 1988 establishes the Australian Privacy Principles (APPs), which regulate areas including collection, use, disclosure, security, access and correction of personal information.
Privacy Act 1988
BotNira's Australian data handling approach is designed with the Australian privacy framework and applicable Privacy Act obligations in mind.
Australian Privacy Principles
BotNira's privacy and security controls are designed to support appropriate handling, protection and management of personal information.
APP 6 — Use & Disclosure
Personal information should be handled consistently with the purposes for which it was collected, subject to applicable exceptions.
APP 8 — Cross-Border Disclosure
Where personal information is disclosed to an overseas recipient, applicable Australian cross-border privacy requirements must be considered.
APP 11 — Security
Reasonable steps should be taken to protect personal information from misuse, interference, loss and unauthorized access or disclosure.
APP 12 & APP 13
Australian privacy principles provide rights and obligations concerning access to and correction of personal information.
Australian storage and international AI processing
Australian vendor data is stored and backed up within BotNira's Australian regional infrastructure.
Certain BotNira functionality requires external AI processing through OpenAI. When those features are used, relevant information may be processed outside Australia.
Australian privacy law contains specific rules regarding cross-border disclosure of personal information. Under APP 8, an APP entity generally needs to take reasonable steps to ensure an overseas recipient does not breach the APPs, subject to applicable exceptions.
BotNira therefore distinguishes between the location of regional storage and the location where a particular AI processing operation may occur.
Security controls protecting Australian data
BotNira uses multiple technical and organizational safeguards to protect information throughout its lifecycle.
SSL / TLS
Secure encrypted connections protect information during transmission.
Encryption at Rest
Stored information is protected using encryption controls.
Encryption in Transit
Data transmitted between systems is protected using secure communication protocols.
Two-Factor Authentication
Additional authentication controls help protect account access.
Firewall & DDoS Protection
Network security controls help protect BotNira infrastructure from malicious traffic.
Vulnerability Scanning
Regular vulnerability scanning is performed to identify potential security weaknesses.
Penetration Testing
Penetration testing has been completed as part of BotNira's security program.
Incident Response
A dedicated security team is responsible for responding to security incidents.
BotNira certifications
BotNira maintains security and compliance certifications supporting its overall security and trust program.
ISO 27001
ISO 27701
SOC 2 Type II
GDPR Compliance
HIPAA
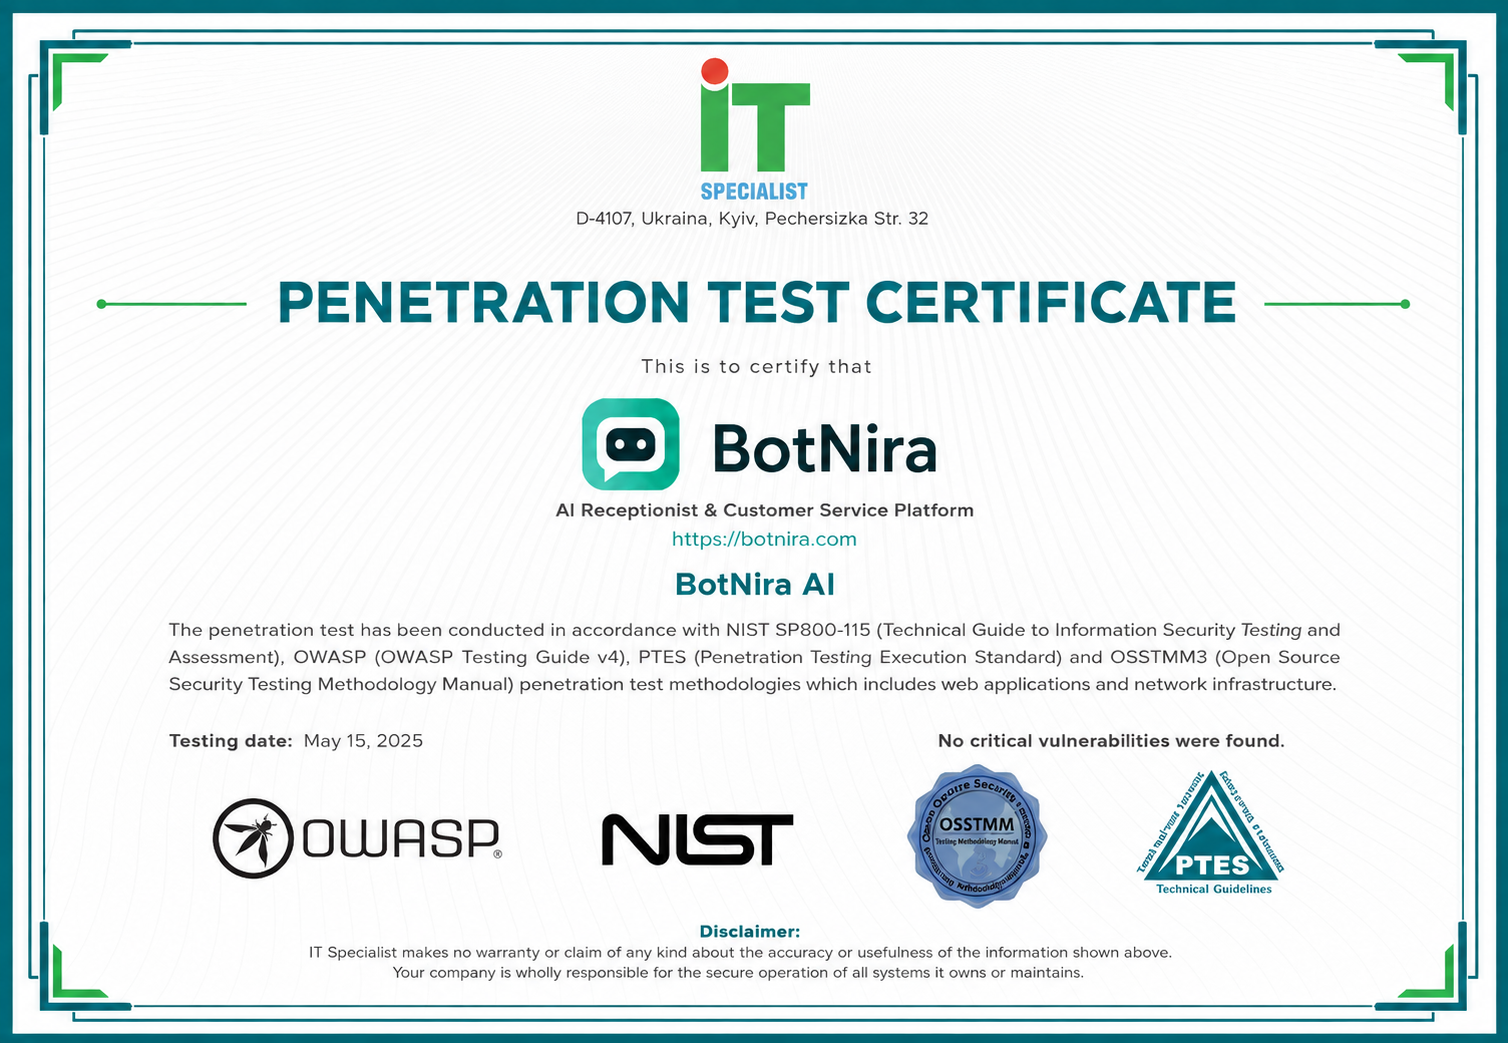
Penetration Testing
Data retention and deletion
While an Australian vendor actively uses BotNira, the vendor can manage and delete its customers' calls, messages and related data through the available BotNira controls.
When a vendor closes its BotNira account, BotNira retains account data for up to 45 days before permanently deleting it.
The retention period provides an operational window for account closure and deletion processes.
Know which providers are involved
BotNira identifies the third-party providers involved in communication and AI functionality.
Australian vendors get Australian regional storage
BotNira's regional infrastructure is designed so that Australian vendor data and backups remain within Australia. External providers are used where required for specific communication or AI functionality.
Australian data residency questions
Is Australian vendor data stored in Australia?
Is AI processing also performed in Australia?
Does BotNira use Twilio for Australian phone calls?
Does WhatsApp involve another provider?
What happens to my data when I close my account?
Can Australian vendors delete customer data?
Does Australian privacy law allow overseas processing?
Does BotNira claim that all Australian data is processed only inside Australia?
Security and transparency come first.
Explore BotNira's security controls, compliance documentation, subprocessors and regional data residency commitments.